
On-prem certificate management, European cloud
Your sensitive data stays on your servers. All customer data and all operation of sslbrain Cloud is in the EU. Cloud runs with the Finnish provider UpCloud.
Why self-hosted
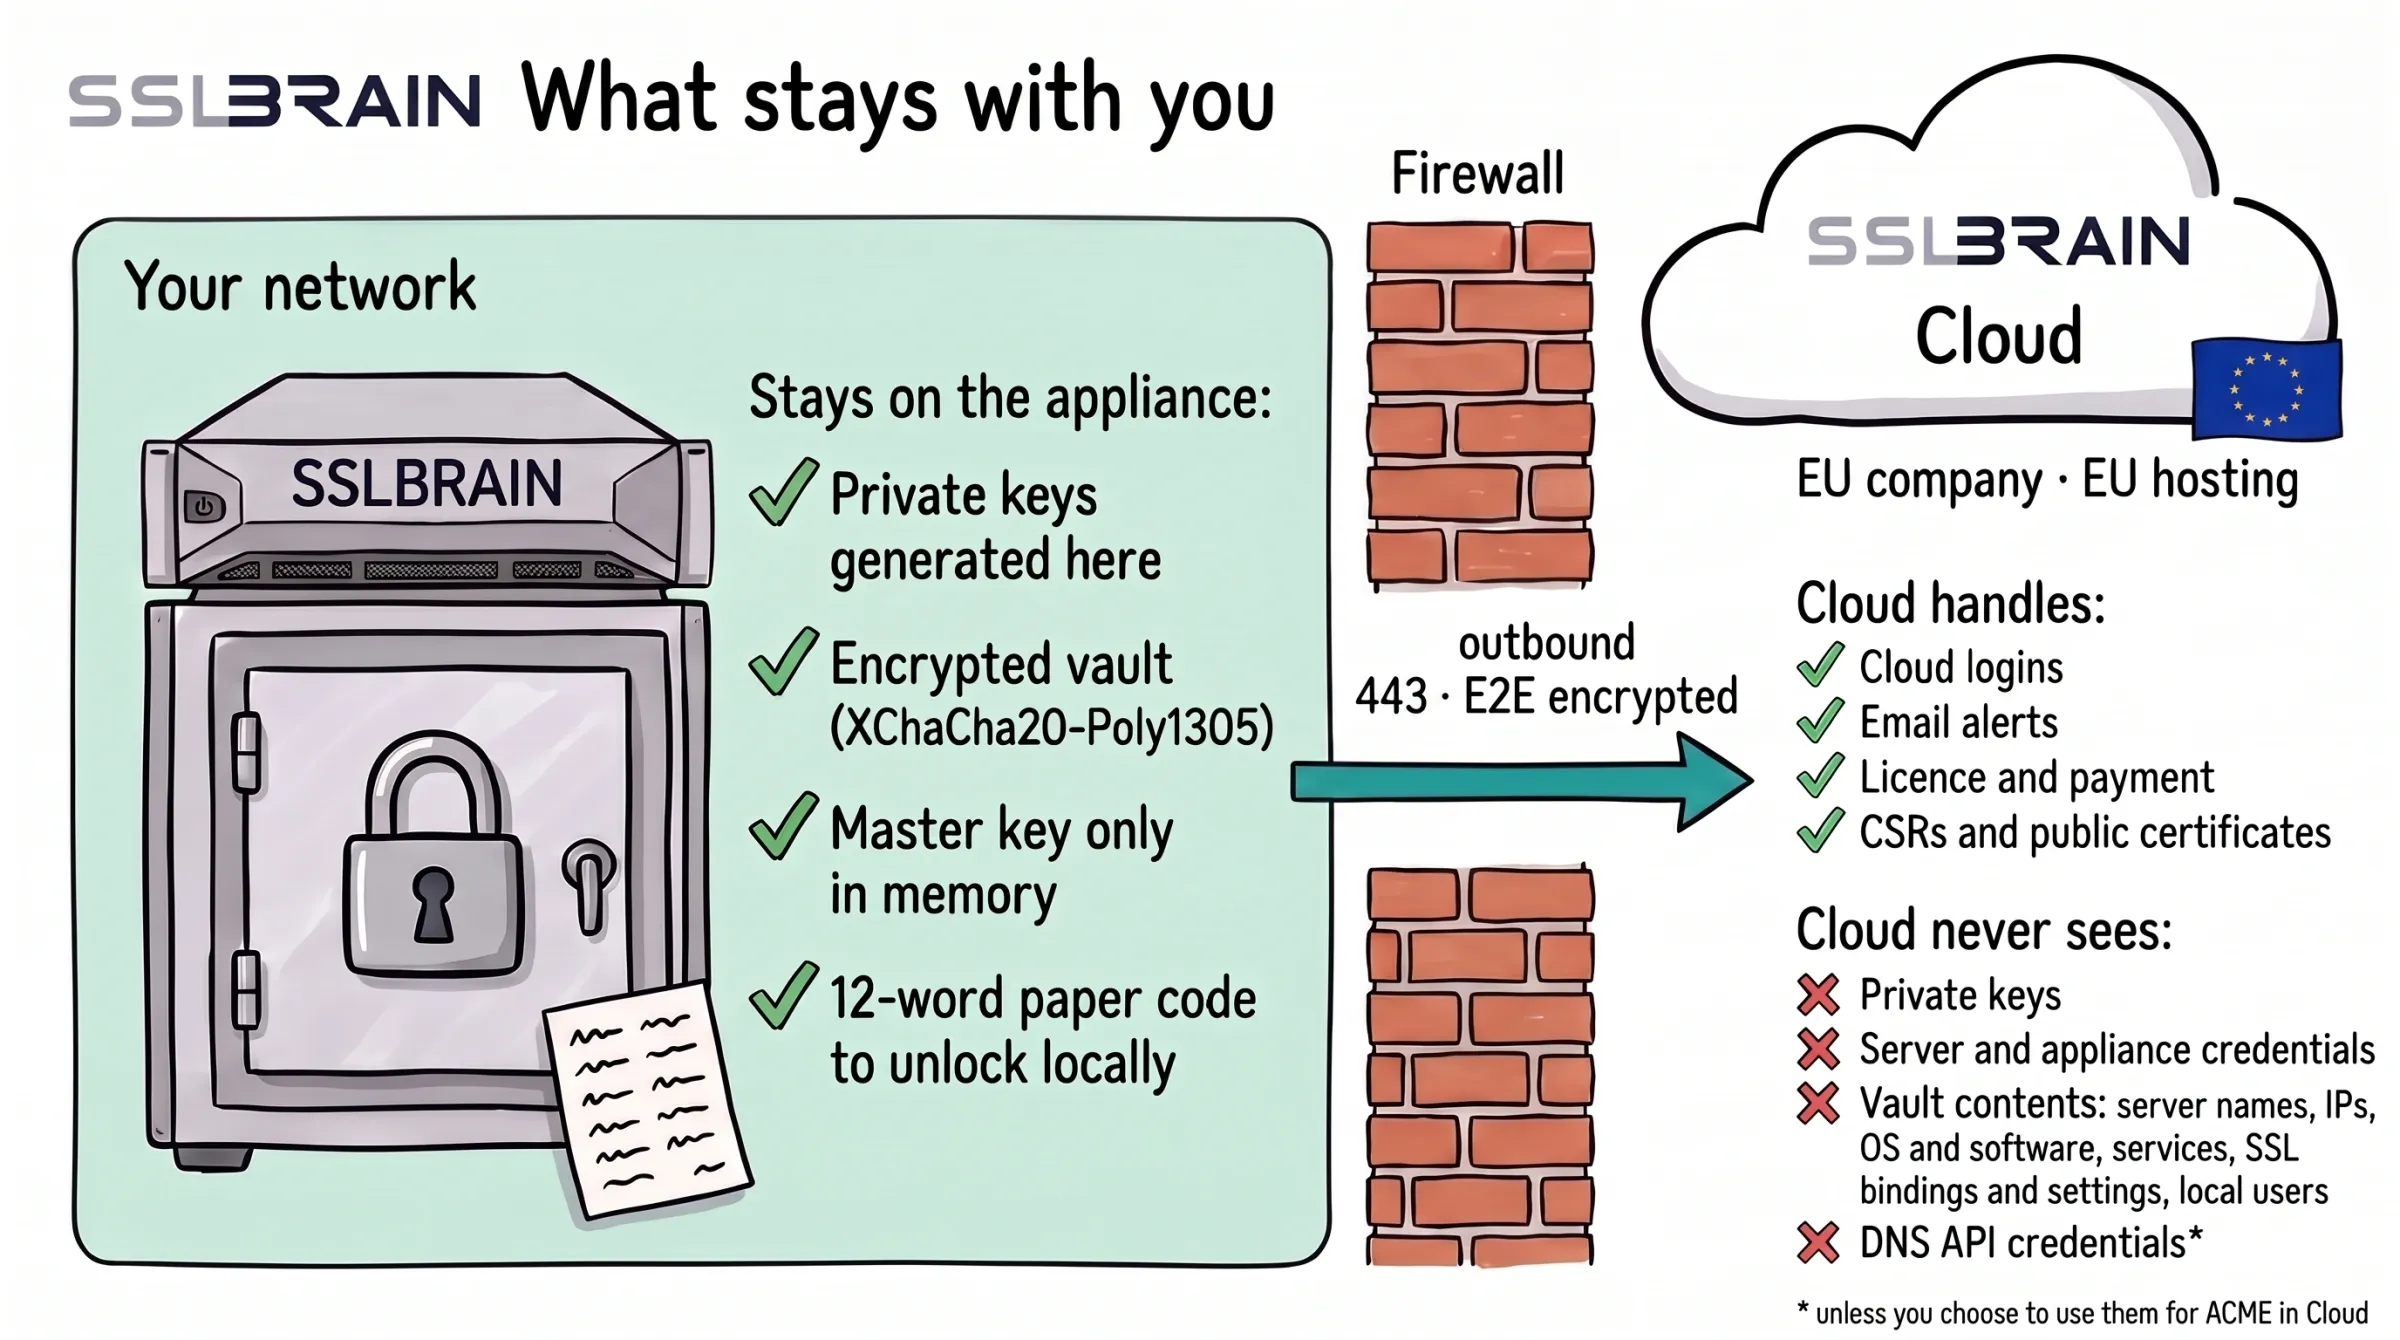
- Stays on the appliance: private keys generated here · encrypted vault (XChaCha20-Poly1305) · master key only in memory · 12-word paper code to unlock locally.
- The appliance talks only to sslbrain Cloud, outbound on port 443 and E2E encrypted. sslbrain Cloud is an EU company with EU hosting.
- Cloud handles: Cloud logins · email alerts · licence and payment · CSRs and public certificates.
- Cloud never sees: private keys · server and appliance credentials · vault contents (server names, IPs, OS and software, services, SSL bindings and settings, local users) · DNS API credentials* (*unless you choose to use them for ACME in Cloud).
Certificate automation requires admin credentials to firewalls, load balancers and servers, including SSH keys, API tokens and DNS API keys. These are credentials with full access to your infrastructure.
Those credentials should not live in a cloud platform that can also reach into your firewalls, load balancers and servers. sslbrain runs inside your network, and no supply chain attack can compromise your server credentials through our infrastructure.
sslbrain Cloud cannot connect to, control, or read data in your sslbrain instance. All communication is initiated from your side.
Stays on your server
sslbrain Cloud handles
Where in the EU
sslbrain Cloud runs on UpCloud, a Finnish infrastructure provider, in five data centers in the EU. The key vault is spread over three of them.
Copenhagen, Denmark
UpCloud dk-cph1
sslbrain Cloud, database, ACME, DNS proxy and registry. Part of the key vault.

Stockholm, Sweden
UpCloud se-sto1
Part of the key vault.

Amsterdam, Netherlands
UpCloud nl-ams1
Part of the key vault.
Helsinki, Finland
UpCloud fi-hel2
Backups.

Frankfurt, Germany
UpCloud de-fra1
Monitoring.
All data centers are certified to ISO 9001, ISO 14001, ISO 22301, ISO 27001, and ISO 50001, as well as SOC 1 and SOC 2 Type II. They operate on 100% renewable energy.
Your local sslbrain instance keeps running regardless of cloud availability. ACME clients running directly against the CA are not affected by a Cloud outage.
Sub-processors
Full transparency about which third parties support FairSSL and sslbrain operations.
| Provider | Location | Purpose | Applies to |
|---|---|---|---|
| UpCloud | Finland (EU), data centers in DK, SE, NL, DE, FI | Hosting, databases, backup, observability | All customers |
| Bunny.net | Slovenia (EU). The files are stored in Germany, and the CDN serves only from EU locations | CDN for static assets | Website visitors |
| Microsoft 365 | EU tenant | Business email and collaboration | Paying and prospective customers |
| Freshdesk | EU-hosted | Support system and ticket handling | Paying customers with support cases |
| Lettermint | Netherlands (EU) | Transactional and notification emails | All customers (including free) |
| Scanpay | Denmark | Payment processing. FairSSL does not receive card data | Paying customers |
| Visma e-conomic | EU/EEA | Accounting and invoicing | Paying customers |
Website analytics on FairSSL and sslbrain sites are collected with Umami, which runs self-hosted in our own EU infrastructure. No third-party analytics are used on customer-facing services.
Certificate Authorities (Let's Encrypt, Google Trust Services, Sectigo, DigiCert, and others) act as independent controllers for certificate issuance under CA/Browser Forum requirements. Domain names in publicly issued certificates are logged in public Certificate Transparency (CT) logs.
Danish SSL company since 2010
FairSSL A/S, CVR 33075782, Denmark. 16 years in the SSL certificate industry.
We deliver certificates to Danish government agencies, defense and emergency services, regions, municipalities, hospitals, energy and telecommunications companies, banks and pension providers, and enterprises of all sizes.
sslbrain is source-available. Your security team can inspect every line of code running on your infrastructure. No black boxes. The Windows agent is delivered as an MSI, and you can build it yourself from the source code.
All customer data and all operation in the EU
All customer data and all operation of sslbrain Cloud is in the EU. Cloud, database, ACME, DNS proxy and registry run in Copenhagen. The key vault is spread over Copenhagen, Stockholm and Amsterdam. Backups are in Helsinki and monitoring in Frankfurt. Email is sent through Lettermint in the Netherlands, and the website is delivered by Bunny in Slovenia.
What is American does not touch customer data: optional sign-in with Google, Microsoft or GitHub, and signing of the Windows installer through Microsoft Azure, which Microsoft requires. Business email (Microsoft 365) and the support system (Freshdesk) are American companies with data in the EU, see the sub-processors above. Invoicing goes through FairSSL's web shop at fairssl.dk, which runs on Amazon Web Services in Frankfurt.
Get started
Download sslbrain and manage your certificates in minutes.